A PCI DSS audit is a detailed examination of the security of an organization's credit-card processing system. The PCI QSA audit consists of both on-site and off-site activities and is performed by a Qualified Security Assessor (QSA) who evaluates an entity's payment and credit-card security implementation against the PCI DSS standard.
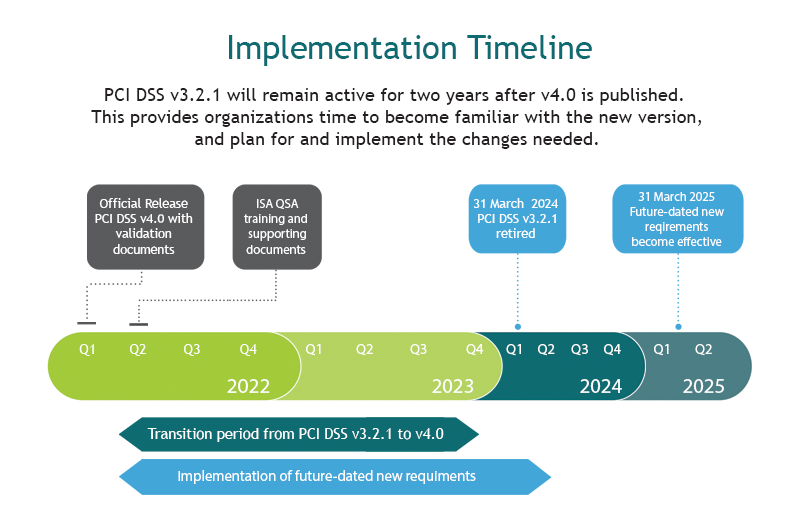
Published in March 2022, version 4.0 of the PCI Data Security Standard replaces version 3.2.1 to address emerging threats and technologies and enable innovative methods to combat new threats.
- Level 1 Service Providers that store, transmit or process more than 300,000 credit card transactions annually.
- Level 1 Merchants that store, transmit or process more than 6,000,000 credit card transactions annually.
- Any other entities required by their acquirer (regardless of annual transaction volume).
On-site Annual Security Audit — a detailed on-site assessment by a PCI SSC certified QSA or ISA, resulting in a RoC and AoC.
External Vulnerability Scan (PCI ASV) — conducted quarterly by a PCI SSC Approved Scanning Vendor on all Internet-facing components that are part of, or provide a path to, the cardholder data environment.
Kickoff and Planning. We discuss the certification process, identify points of contact, agree timelines and define a project roadmap.
Preparation Phase. A tailored support approach which can include: PCI DSS training/workshop; PCI DSS scoping (network segmentation, third-party dependencies); a Pre-Assessment or full Gap Assessment; and remediation/advisory support.
Formal validation. Once all controls are confirmed in place, the on-site assessment begins.
Reporting. Delivered within 3 weeks of successful completion.
Deliverables: PCI DSS RoC (Report on Compliance), PCI AoC (Attestation of Compliance), and a Certificate of Compliance.
Continual Support. Ongoing maintenance of compliance and guidance on standard changes.
You may also be interested in:
- PCI QSA Audit — examination of IT systems, documents, policies, procedures and interviews at the client's premises for PCI DSS compliance.
- PCI ASV Audit — services checking the security level of external information systems per PCI DSS.
- GAP Audit — testing the degree of compliance of the client's system with PCI DSS.
- RoC — Report on Compliance. AoC — Attestation of Compliance. AoSC — Attestation of Scan Compliance.
- SAQ — Self Assessment Questionnaire. CoC — Certificate of Compliance (issued by SC2labs for PR purposes).